- Home
- Documentation
- Evidence chain and reports
Documentation
Evidence chain and reports
A ledger that can only grow, anchored publicly every day and recomputable by your auditor. Plus the quarterly report with the mapping to NIS2, ISO 27001, CyFun, DORA and GDPR.
The ledger
Everything Zekura does becomes a record in your organisation's evidence chain: every snapshot, every verification, every restore, every maintenance pass, every change to users or jobs. Every record contains the hash of the previous one and is signed with the platform's key. Change one digit anywhere, and everything from that record on breaks.
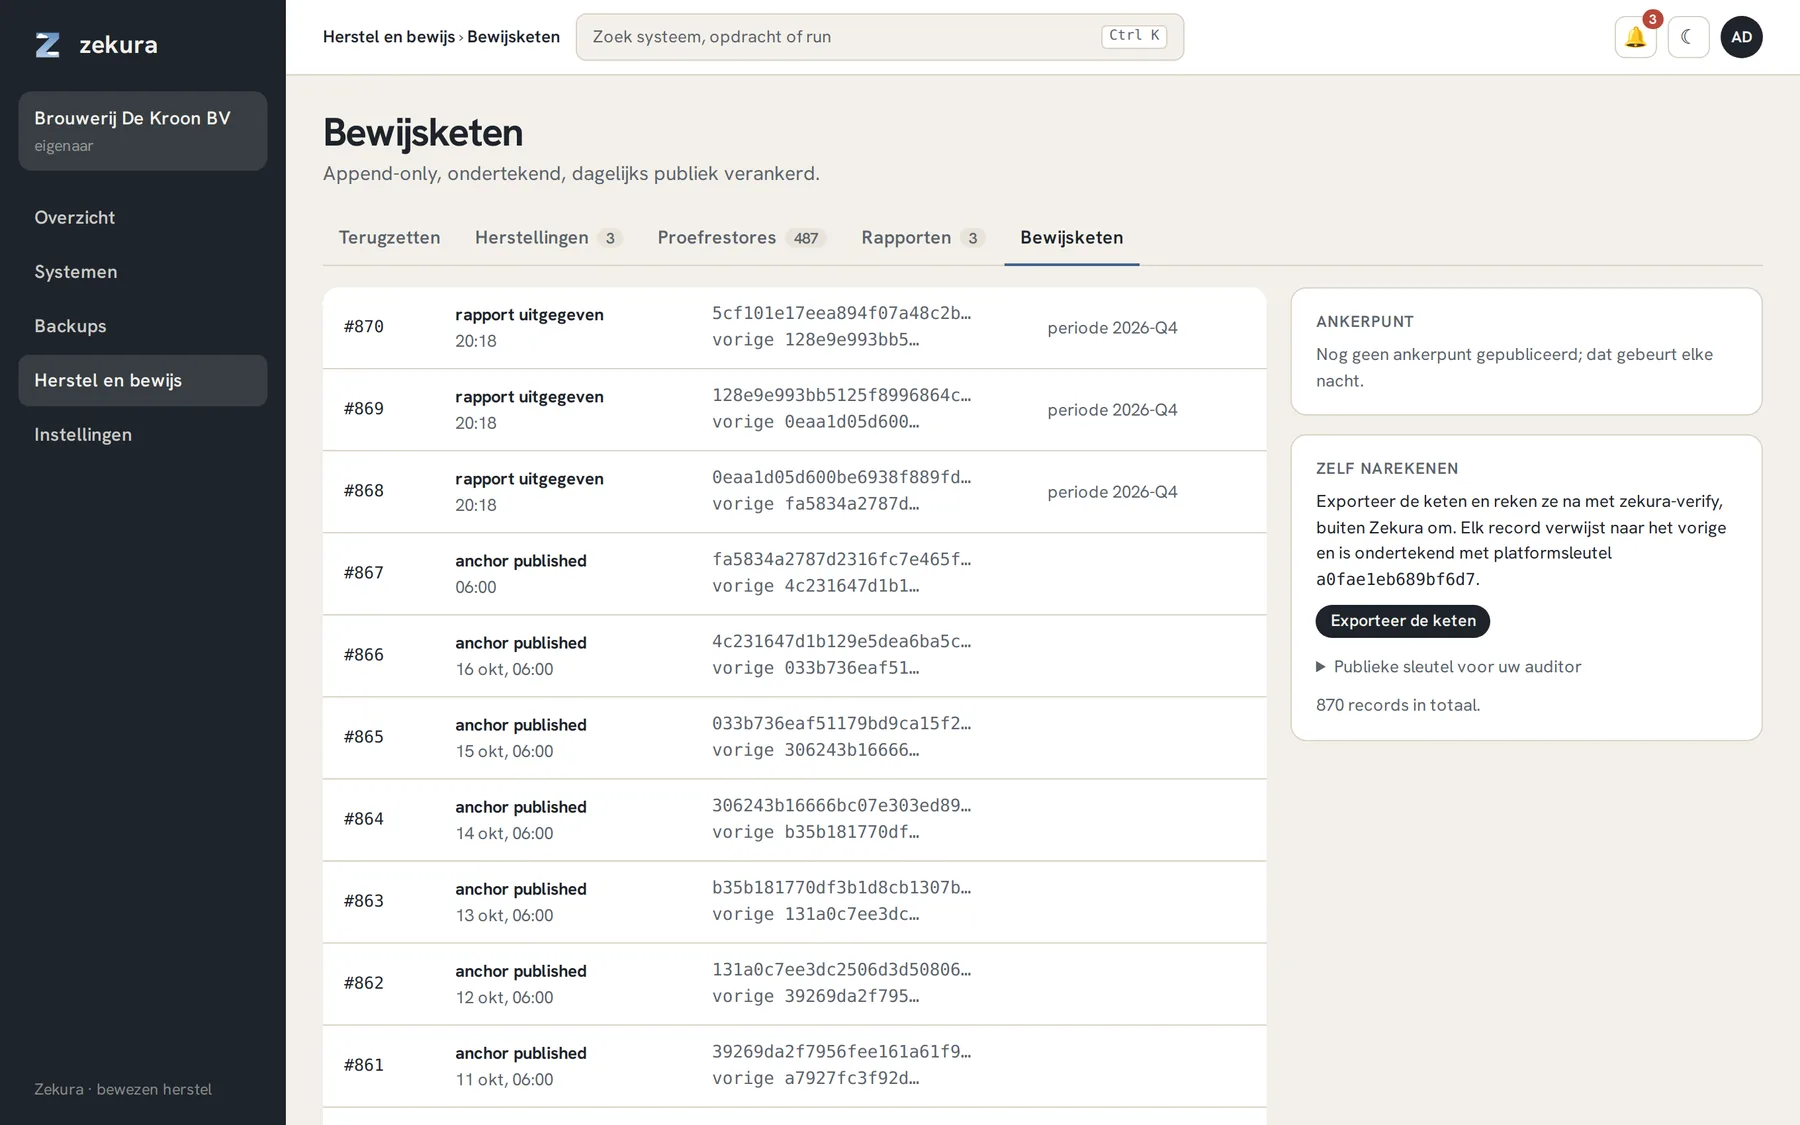
The chain of a new organisation starts at record 1. Nothing is visible across the boundary of an organisation.
Anchored publicly every day
Every day the last hash of every chain is published in the public repository git.gotrust.be/gotrust/zekura-roots: only checksums and public keys, no names or data. In git, with timestamps and a history that even we cannot rewrite without it being noticed. Whoever has yesterday's hash can later prove that nothing was rewritten.
Recompute it yourself
Export the chain gives a JSON file with all records and the platform's public keys. Recompute it with zekura-verify, a standalone tool without dependencies that an auditor can read in five minutes:
npx tsx zekura-verify/verify.ts zekura-chain-<organisation>.json --root <hash from the publication>
It checks per record the hash of the content, the reference to the previous record, the signature and the continuous numbering. There is also a static binary with the same checks. The public key is on the chain page; give it to your auditor.
The report for the auditor
Recovery and evidence → Reports → Issue report produces a quarterly or monthly report as PDF, in Dutch, French or English.
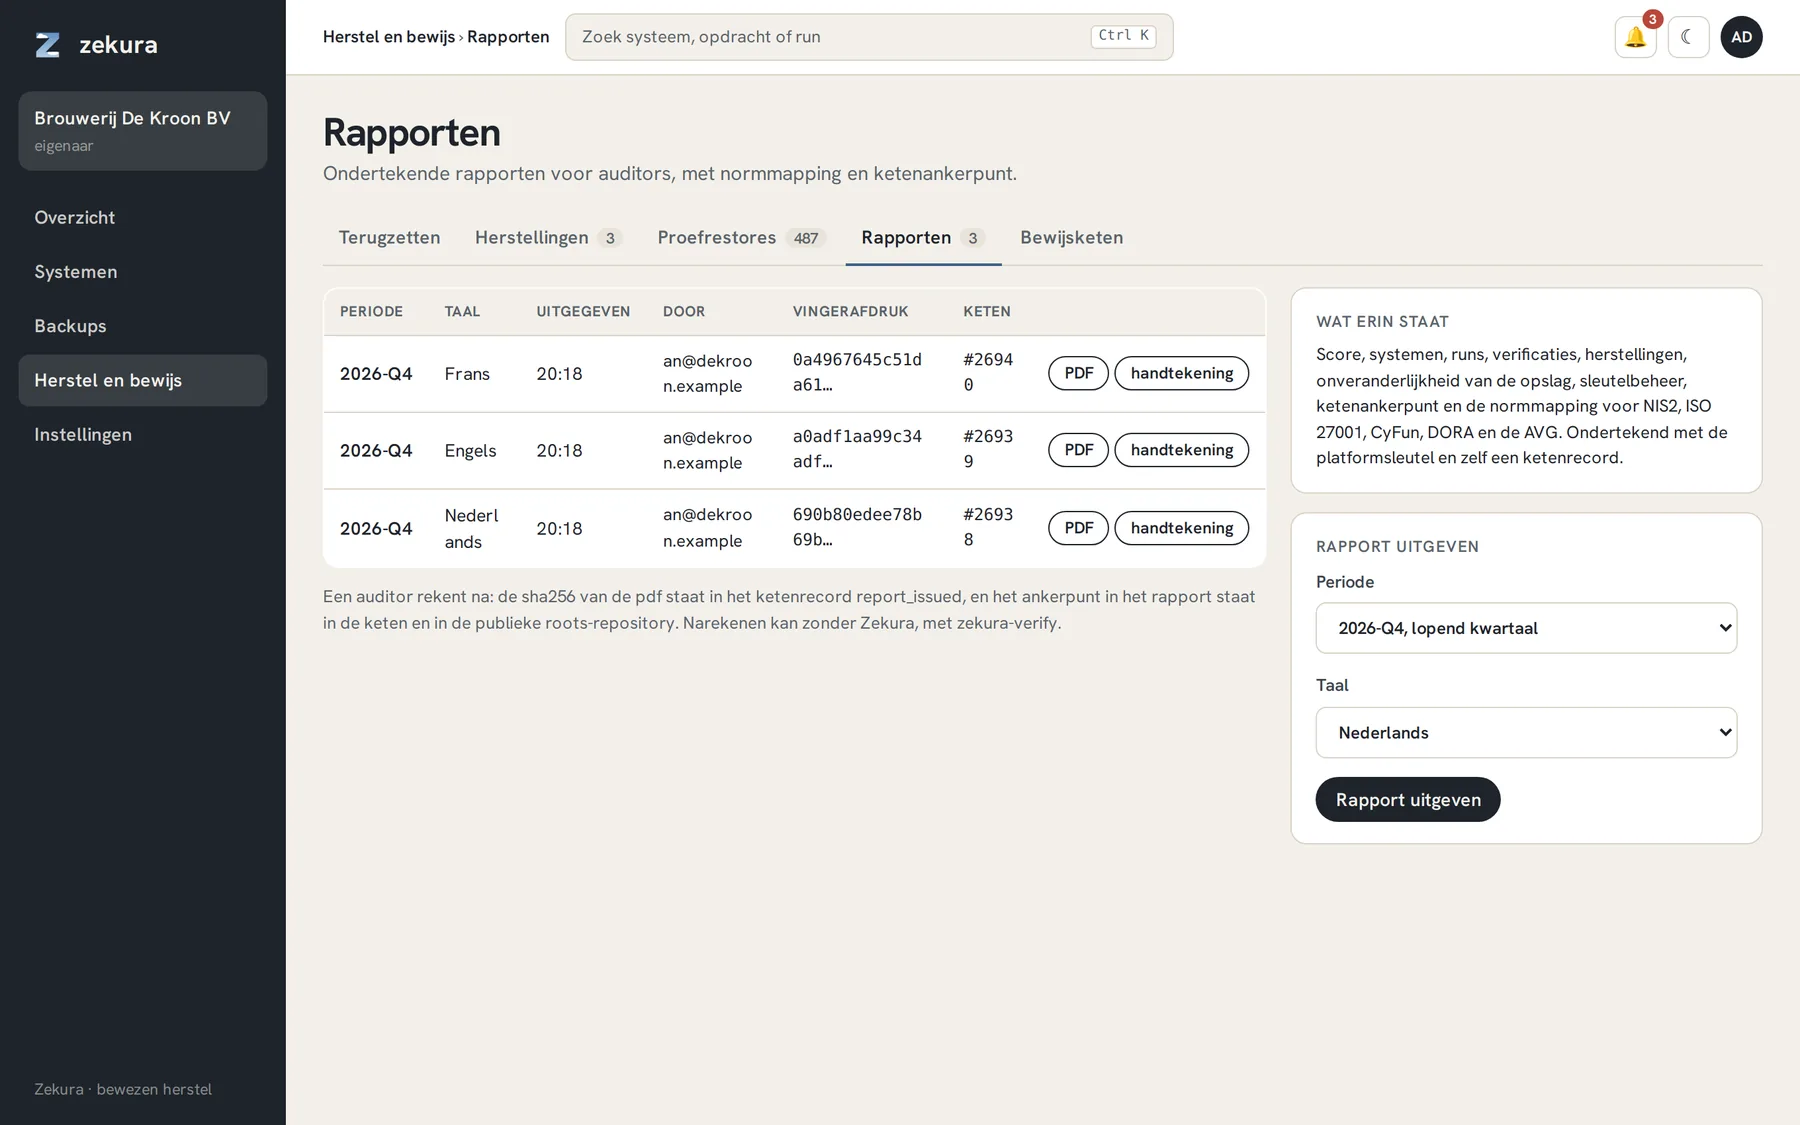
What it contains: the Restore Assurance Score, the protected systems with their last successful run, runs and verifications per level, restores with measured recovery time, storage and immutability per destination, the key model and the escrow test, and the chain anchor at the end of the period. Then the norm mapping: for every requirement from NIS2 article 21(2)(c), ISO/IEC 27001:2022 A.8.13 and A.5.30, CyFun PR.IP-4, DORA articles 11 and 12 and GDPR article 32(1)(c), which evidence is in the report and whether the requirement is met, partially met or not met. Judged on the facts of the period, not on promises.
The report is evidence itself: the sha256 of the PDF is signed and recorded as a chain record. An auditor recomputes it with three steps printed on the last page.